Gaps live in configuration
Many failures are configuration and coverage gaps mistaken for a missing product. Licenses without tuning leave the same risk on the table.
Three disciplines. One architecture. Zero gaps.
The expertise to design it. The engineers to run it.
24/7 US-based operationsArrow delivers layered messaging security with ongoing tuning and response, for the channel attackers still use first.
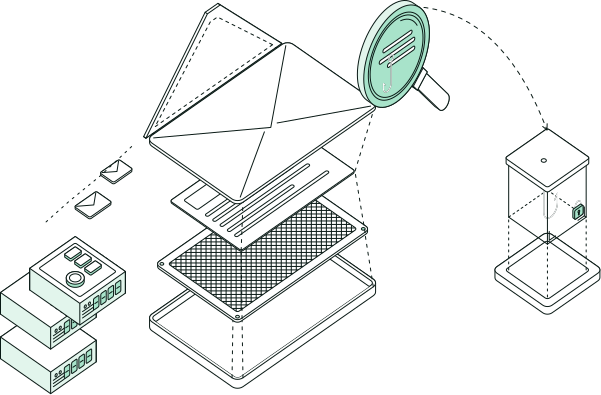
We layer defenses across every inbound and outbound message.
We continuously tune protection as new threats emerge.
Email is still attackers’ first move, so we run it as an operated control.
Because business email compromise often moves money without malware. Compromised mailboxes create rules, forwarding, and silent collection, and impersonation or delegation abuse looks like normal collaboration until the damage is done.
Many failures are configuration and coverage gaps mistaken for a missing product. Licenses without tuning leave the same risk on the table.
We watch for account takeover patterns, malicious mailbox rules, and unauthorized delegation, along with bad URLs.
Detection has to reach operators who can investigate and contain.
Layered filtering matters. So do mailbox-compromise detection, triage that respects your people, and a response path that doesn’t bounce between vendors.
What Arrow delivers
Layered inbound filtering and outbound control for mail and collaboration, plus detection of the mailbox compromise a filter doesn’t catch. Investigation and containment run with operators who know your tenant.
Tied to identity
Because messaging compromise often is identity compromise. Messaging Security stays on the same floor as Identity Security and Endpoint Security, so an email incident moves to containment without a handoff between vendors.
Why Arrow
Because many “tool gaps” are configuration gaps. Arrow tunes policy against your threat profile on a named team, so false positives and missed threats are handled as routine operations work.
What BEC looks like
past the link.
Business email compromise and mailbox abuse often look like normal collaboration. These are the patterns the program watches for.
Configuration and coverage come first, because that’s where many messaging programs fail.
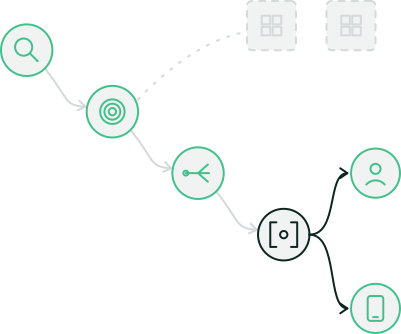
Assess
We assess current mail protection, starting with configuration and coverage gaps.
Harden configuration
Policies are tuned to how the tenant actually works, closing the gaps that make good tools fail.
Monitor
We watch for BEC and phishing patterns, including mailbox rules and delegation.
Investigate and contain
Operators who know the tenant investigate and contain, so an email incident ends in containment and hardening.
Feed lessons back
Lessons improve your identity and Endpoint Security programs, aligned with Managed Microsoft 365 and Managed Microsoft Security when those are in scope.
Access policy that follows the user, watched by the same floor.
Operated policy and response on every device that touches the estate.
Detection and response from the same operators, every time.
Hardened firewalls and segmentation across the fabric you run.
Operated Microsoft security controls alongside messaging, identity, and endpoint when the Microsoft stack is in scope.
It covers inbound filtering and outbound control for mail and collaboration, with tuning after go-live. The program is operated posture that keeps adjusting.
Failures are often configuration and coverage gaps. Licenses without operators and without tuning against your threat profile leave the same risk on the table.
Arrow, against your threat profile, on a named team, so false positives and missed threats are treated as routine operations work.
Messaging, identity, and endpoint sit on the same architecture, so response is not a handoff between vendors. One accountable floor when Arrow runs the related controls.
No. The work protects mail and collaboration paths you already use. Platform replacement is out of scope unless the tool itself cannot support the required controls.